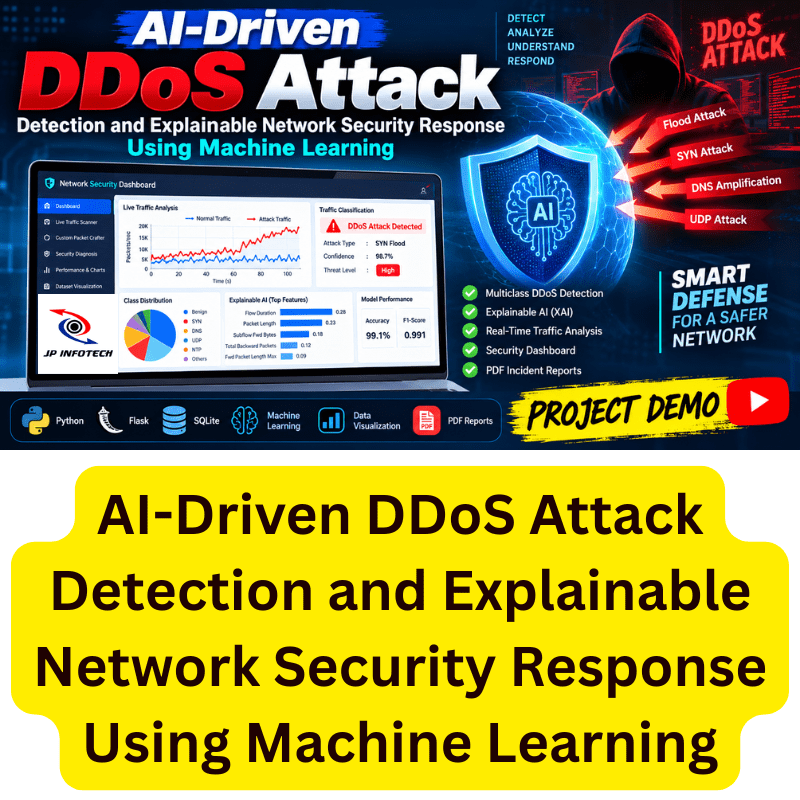
AI-Driven DDoS Attack Detection and Explainable Network Security Response Using Machine Learning
AI-Driven DDoS Attack Detection and Explainable Network Security Response Using Machine Learning
IEEE BASE PAPER TITLE:
A Deeper Look on Explanation Methods for Deep Learning Models on Raw-Based Traffic of DDoS Attacks
IEEE BASE PAPER ABSTRACT:
With the increasing prevalence of DDoS attacks, various machine learning-based detection models have been employed to mitigate these malicious behaviors. Understanding how machine learning models function can be quite complex, especially for intricate and nonlinear models like deep learning architectures. Recently, various techniques have been advanced to interpret deep learning models and address issues of ambiguity. In this paper, we present a comprehensive analysis of various explanation methods that are applied to Long Short-Term Memory (LSTM) model for detecting Distributed Denial of Service (DDoS) attacks on raw traffic data. While previous studies have focused primarily on improving detection accuracy on feature-based datasets, this paper emphasizes the importance of interpretability in deep learning models on raw-based traffic datasets. By employing explanation techniques such as LIME, SHAP, Anchor, and LORE, we provide insights into the decision-making processes of LSTM models, thereby enhancing trust and understanding in classifying DDoS attacks. The use of raw-based network traffic revealed crucial packet fields that played an important role behind the true and false positive predictions of the LSTM model, as well as identifying common network fields among the DDoS attacks to justify the misclassifications between similar DDoS attacks.
PROJECT OUTPUT VIDEO:
ALGORITHM/ MODEL USED:
LSTM
OUR PROPOSED PROJECT ABSTRACT:
Distributed Denial-of-Service (DDoS) attacks are among the major cybersecurity threats that can disrupt network services by generating large volumes of malicious traffic and exhausting the resources of targeted systems. The increasing complexity and diversity of modern DDoS attacks make conventional rule-based and signature-based security mechanisms less effective in identifying previously unseen or sophisticated attack patterns. Therefore, intelligent network security solutions capable of detecting different types of malicious traffic, explaining detection decisions, and supporting rapid security responses are increasingly important. This project presents AI-Driven DDoS Attack Detection and Explainable Network Security Response Using Machine Learning, an intelligent web-based security framework designed to detect and classify DDoS network traffic while providing interpretable security analysis and response information.
In the proposed system, Python serves as the main programming language while Flask serves as the framework for the web application development. HTML, CSS, and JavaScript serve as the tools for designing an interactive interface whereas SQLite manages application data. The ML module is designed using CICDDoS2019 that consists of network flow data with respect to various DDoS attacks. Training is performed through loading the dataset from Parquet file format with batch-based approach and sampling 20% of the training dataset that amounts to 5,492,553 network flow data. The system drops non-predictive features, encodes categorical data, treats missing and infinite data, standardizes numerical features and performs statistical feature selection based on ANOVA scoring method. Of the initial 91 predictive features, the system selects 28 important features.
For intelligent DDoS detection, the system employs a Long Short-Term Memory (LSTM) deep learning model configured for multiclass network traffic classification. The model consists of two LSTM layers with dropout and batch normalization, followed by dense layers and a softmax output layer for classification. The model is trained using the Adam optimizer and sparse categorical cross-entropy loss. The trained model is capable of distinguishing multiple network traffic categories, including benign traffic and attack classes such as DrDoS DNS, DrDoS NTP, DrDoS SNMP, DrDoS SSDP, LDAP, MSSQL, NetBIOS, Portmap, SYN, TFTP, UDP, and UDPLag. The training implementation uses a 70:30 training-testing split and five training epochs.
The Flask-based frontend provides an interactive Security Operations Center (SOC) dashboard through which authenticated users can access the network security functions. The system provides a Live Traffic Ingress Scanner that allows users to simulate random, benign, or malicious network flows and submit the intercepted traffic for security diagnosis. A major component of the developed framework is its Explainable AI (XAI) security diagnosis module. Instead of displaying only the predicted attack class, the system presents the classification result, threat severity level, predicted confidence, and feature abnormality information to help users understand why network traffic was identified as suspicious. The system also supports generation of a print-ready one-page PDF security incident report containing the diagnosis information.
Overall, the proposed system integrates machine learning-based DDoS detection, multiclass attack classification, explainable security diagnostics, interactive traffic simulation, and automated SDN-oriented response information into a unified Flask-based web application. By combining intelligent detection with interpretable analysis and security response capabilities, the system provides a practical framework for understanding and responding to DDoS-related network threats while also offering useful visualization and reporting features for security monitoring and analysis.
SYSTEM REQUIREMENTS:
HARDWARE REQUIREMENTS:
- System : Pentium i3 Processor.
- Hard Disk : 20 GB.
- Monitor : 15’’ LED.
- Input Devices : Keyboard, Mouse.
- Ram : 8 GB.
SOFTWARE REQUIREMENTS:
- Operating System : Windows 10 / 11.
- Coding Language : Python 3.13.15.
- Web Framework : Flask.
- Frontend : HTML, CSS, JavaScript.
- Database : SQLite.
REFERENCE:
Basil AsSadhan, Abdulmuneem Bashaiwth, Hamad Binsalleeh, “A Deeper Look on Explanation Methods for Deep Learning Models on Raw-Based Traffic of DDoS Attacks”, IEEE Transactions on Machine Learning in Communications and Networking, Volume 4, 2026.
👉CLICK HERE TO BUY THIS PROJECT “AI-Driven DDoS Attack Detection and Explainable Network Security Response Using Machine Learning” SOURCE CODE👈
FAQ’s & Answers:
The main objective is to develop an intelligent network security framework capable of analyzing network traffic, detecting and classifying DDoS attacks using machine learning, and providing explainable information about the model's prediction through an integrated web-based security dashboard.
A Distributed Denial-of-Service (DDoS) attack is a cyberattack in which large volumes of traffic are directed toward a target system or service from multiple sources. The excessive traffic can consume network bandwidth and system resources, preventing legitimate users from accessing the service.
DDoS attacks can seriously affect the availability of online services by overwhelming computational resources and network bandwidth. Therefore, identifying malicious traffic and distinguishing it from legitimate traffic is an important network security requirement.
The project uses the CICDDoS2019 dataset, which contains network traffic associated with different categories of DDoS attacks. The research foundation also uses CICDDoS2019 for multiclass DDoS traffic analysis.
CICDDoS2019 provides network traffic representing multiple DDoS attack categories, making it suitable for developing a multiclass DDoS detection model. The source research describes approximately 12 DDoS traffic classes in the dataset.
DDoS traffic can exhibit patterns across sequences of network packets. LSTM networks are designed to process sequential information and maintain dependencies over time, making them suitable for analyzing traffic patterns associated with DDoS attacks.
The proposed system performs several preprocessing operations, including: Removal of non-predictive attributes Handling missing values Handling infinite values Label encoding Numerical feature processing Feature scaling using StandardScaler ANOVA-based feature selection
Feature selection identifies the most relevant network traffic attributes for classification. In this project, the feature space is reduced from 91 predictive features to 28 selected features, reducing unnecessary input information before classification.
Explainable AI refers to techniques that help users understand why a machine learning model produced a particular prediction. This is particularly important for cybersecurity applications because analysts need to understand the factors contributing to a detected threat. The research foundation highlights the importance of interpreting deep learning decisions because of the black-box nature of many deep learning models.
The base research investigates LIME, SHAP, Anchor, and LORE for explaining LSTM predictions. The implemented project interface presents XAI feature abnormality scoring and classification confidence information as part of its diagnostic workflow.
The system can provide: Network traffic classification DDoS attack category XAI feature abnormality information Multiclass confidence probabilities Security diagnosis information Performance charts Dataset distribution charts PDF security incident reports
The Performance module provides: Training accuracy Validation accuracy Training loss Validation loss Per-class evaluation Confusion matrix ANOVA feature rankings These features allow the performance of the trained model to be examined through the web interface.
Yes. The project contains several research-oriented components, including multiclass DDoS detection, LSTM-based deep learning, feature selection, explainable AI, network traffic analysis, and performance evaluation. These components can provide a basis for preparing a research paper, provided that the experimental methodology, results, comparison with existing approaches, and contribution are appropriately documented. You can contact JP INFOTECH for International Journal Publication, Conference Publication or Scopus Publication. What is the main objective of the project?
What is a DDoS attack?
Why is DDoS attack detection important?
What dataset is used in this project?
Why is CICDDoS2019 selected?
Which machine learning model is used?
What preprocessing techniques are used?
What is the purpose of feature selection?
What is Explainable AI (XAI)?
Which XAI techniques are associated with the research foundation?
What type of output does the system provide?
What are the performance evaluation features?
Can this project be used for research publication?